Software Testing Checklist: What Belongs on It, Phase by Phase
This software testing checklist groups every item by the phase of the test process it belongs to, marks the items teams routinely skip, and shows how to wire the lis…
Proactively identifying and mitigating vulnerabilities to safeguard against cyber threats.
SEE WHAT WE DO




Simulates an attack on a system to identify vulnerabilities and assess the effectiveness of security controls.

Automated process that identifies vulnerabilities in systems, networks and applications.

Assesses the security of a network and identifies vulnerabilities in network infrastructure.

Assesses the security of web applications and identifies vulnerabilities in the application code and underlying infrastructure.

Evaluates a system or organization's compliance with industry and government security regulations and standards.

Simulates real-world social engineering attacks to assess an organization's security awareness and preparedness.

Identifies vulnerabilities in the source code of an application

Identifies vulnerabilities in the underlying infrastructure of a system or network.

Identifies vulnerabilities in wireless networks and devices.

Identifies vulnerabilities in mobile applications and devices.
 Web Applications
 Websites
 Mobile Applications
There are several standards and best practices that organizations can use as guidelines for security testing. Some of the most widely recognized standards include:

OWASP provides a list of the top 10 most critical web application security risks and offers guidance on how to prevent and mitigate these risks.
NIST provides a wide range of guidance on cybersecurity, including best practices for security testing.
This standard applies to organizations that accept credit card payments and includes requirements for regular security testing.
This international standard provides a framework for information security management and includes guidelines for security testing and assessment.
SOC 2 is a security standard that audits and certifies a company's information security controls.
Security testing is a process of evaluating a system or application to identify potential vulnerabilities and assess the effectiveness of security controls. The specific methods used in security testing can vary depending on the system or application being tested, the organization's security requirements, and the goals of the testing. However, some common methods used in security testing include

This method involves using automated tools to scan a system or application for known vulnerabilities. These tools can identify missing patches, misconfigurations, and other issues that could be exploited by attackers.

This method involves attempting to exploit identified vulnerabilities in a system or application to determine the potential impact of a successful attack. Penetration testing can be performed using manual or automated methods.

This method involves evaluating the likelihood and impact of potential security threats to a system or application. The results of a risk assessment can be used to prioritize the testing of specific vulnerabilities or security controls.

This method involves reviewing the source code of an application to identify any vulnerabilities or weaknesses. This process is done by security experts and is used to identify vulnerabilities that may not be identified through other types of testing.

This method involves simulating real-world attacks on employees through email, phone, or in-person to test their awareness and readiness to prevent a real attack.

This method involves testing a system or application against industry-specific compliance standards such as HIPAA, SOC 2, PCI-DSS, etc.


Don't wait for a security breach to happen, schedule your consultation with us today and safeguard your systems and applications. Contact us now to secure your digital assets.

Vervali was commissioned to audit, identify and remedy over 2,000 URLs across all client platforms and solutions in accordance to the WCAG 2.0 guidelines with the objective to achieve AA Level of the 508 certifications.
Download
The offer loading and IP whitelisting was a process that was managed internally by our client. When they struggled to manage the increased volume, they reached out to us for help with manual data entry. Vervali analyzed the entire manual process and produced an automation plan and framework.
Download

To sustain an intensely competitive landscape of frequent flyers and loyalty programs our client was making every effort to engage & retain its customers by introducing increased benefits and new products. However, the introduction of these new changes without proper testing made their website more vulnerable and multiple defects.
Download
With the increasing customer base, our client was enjoying great traffic and demand for their software. However, to sustain this increased growth, our client knew that they had to constantly upgrade their product. While they had introduced software to digitize the employee onboarding process. However, there were still many manual processes still in play. Our client needed a strategic partner, who can act as an extension of their team and help them digitize the manual processes.
Download

Nilesh has been our go to person for QA since we started our business. The quality of his work and the other resources we've been assigned through him have always been outstanding! If anyone ever needs to setup a QA team to fully test an application I recommend going with Nilesh and his company.
I was always impressed with their feedback and will to improve things for the better. The success of the business depends on the successful QA efforts the vendor has provided. The team members, including their leadership, are reliable and easy to collaborate with. Their professional communication style and efficient workflow are commendable.
The clients are happy with the quality of the product that was delivered. Vervali Systems Pvt. Ltd. worked hard to complete everything within a short timeframe. Their team is flexible and friendly, making the engagement a positive experience.
Vervali Systems Pvt. Ltd. has helped to make the solutions virtually bug-free while substantially improving the designs. We really appreciate their transparent and frank communications.
Internal stakeholders are pleased with Vervali Systems Pvt. Ltd's QA services. They maintained a smooth workflow throughout the timeline supported by their prompt bug reports. They ensured stakeholders were always well-informed about their progress.
OUR BLOGS
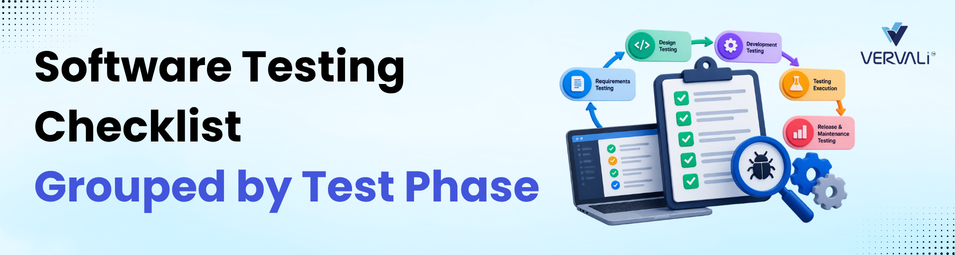
This software testing checklist groups every item by the phase of the test process it belongs to, marks the items teams routinely skip, and shows how to wire the lis…
This guide explains what a QA maturity assessment scores you against, what the deliverable looks like on the last day, and when advisory work is the wrong purchase.
This guide explains what mobile app testing services cover, how to size a device matrix from United States traffic data, and what Apple and Google check before a rel…

This guide prices the five QA outsourcing engagement models against the cost of an in-house hire, and names the situations where outsourcing is the wrong call.
This article ranks nine software testing companies on their verified review evidence and engagement floors, and sets out the criteria before the ranking.
A ranked comparison of ten IT staff augmentation vendors on verified Clutch data, with the ranking criteria stated before the list. Covers why the highest-rated firm…
Penetration testing is priced by tester-days multiplied by a day rate, plus reporting and retest. This guide sets out the seven variables that move a quote, how to e…
A dedicated development team is a contract for a named group of engineers who work only on your product, with the vendor carrying employment, replacement and infrast…

Our Expertise


Trusted by 150+ Leading Brands

A Strong Team of 275+ QA and Dev Professionals

Worked across 450+ Successful Projects
 Email Us
 Call Us
From flawless code to flawless quality - we design, develop, and test digital solutions that deliver real results.